 | The steps on this page are considered risky for your console, as there is a chance you can brick it. Please have someone else mod your console if you are not experienced in soldering! |
EXT_CLK is a modern & open source RGH method by Octal450 that uses the EXT_CLK_EN point instead of CPU_PLL_BYPASS to allow reliable glitching of Xenon and Zephyr Xbox 360 consoles.
Equipment Needed
- A compatible glitch chip:
- Coolrunner Rev A/B/C/D
- Matrix Glitcher
- X360ACE V1/V2/V3
- It is highly recommended to use STBY_CLK instead of a glitch chip's built in oscillator with EXT_CLK, but if you wish to install a crystal on a glitch chip or use a chip's preinstalled crystal it's best to use a 48 MHz one.
- A PC running Windows Vista or later
- A soldering iron, solder, flux, and isopropyl alcohol with cotton swabs
- A NAND & glitch chip flasher
- J-Runner with Extras version 3.4.0 or later (Includes EXT_CLK Matrix/CoolRunner Timings)
- EXT_CLK Timing Files (X360ACE chips only)
- A NAND backup with XeLL written to the console
Reading Your NAND
Bad Update
With the Bad Update hypervisor exploit, it is entirely possible to get a NAND and CPU key dump from an Xbox 360 without even soldering to the console. This can end up saving a lot of time during the mod process, as you don't need to mess with soldering up a NAND flasher for a NAND dump & flash a XeLL image with an RGH installation to decrypt your NAND anymore. You can just do a NAND dump, decrypt it with the CPU key dumped with Simple 360 NAND flasher or XellLaunch, and directly create a Glitch2 RGH 3 NAND image that you can flash to the console.
You can use the homebrew apps for flashing the NAND as well, but this is strongly discouraged unless you already own a NAND flasher that you can use to recover from a bad NAND image (seen below).
NAND Flashing Hardware
There are a few different tools for reading your NAND chip: xFlasher 360, Nand-X, JR Programmer, Matrix USB NAND Flasher, PicoFlasher, or a LPT cable. Consider the pros and cons below and choose the method that’s right for you. An LPT cable is not recommended as it's extremely slow, requires more work than other options, and cannot be used to program glitch chips.
A guide on how to dump and write to a standard NAND can be found here.
| Device | Pros | Cons |
|---|---|---|
| xFlasher 360 |
|
|
| PicoFlasher |
|
|
| 4GB USB Tool |
|
|
| SD Card Tool (any brand) |
|
|
| Nand-X |
|
|
| Matrix USB NAND Flasher |
|
|
| LPT Cable |
|
|
Programming the Glitch Chip
- Plug the cable from your programmer into the chip programmer.
- If you are using an xFlasher, ensure the switch is set to
SPI. - CoolRunner: Slide switch to "PRG".
- If you are using an xFlasher, ensure the switch is set to
- Open J-Runner with Extras. Click "Program Timing File" in the upper left and select your console’s tab and the relevant radio button for EXT_CLK.
- You can use the timing assistant in the bottom left to auto select a safe timing for your motherboard revision.
- Click "Program". When complete, unplug the cable from the glitch chip.
- CoolRunner: Set the switch back to "NOR".
Glitch Chip Installation
Motherboard points
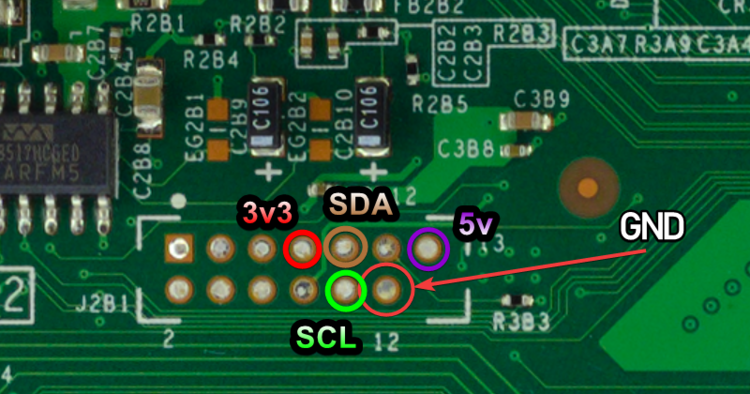
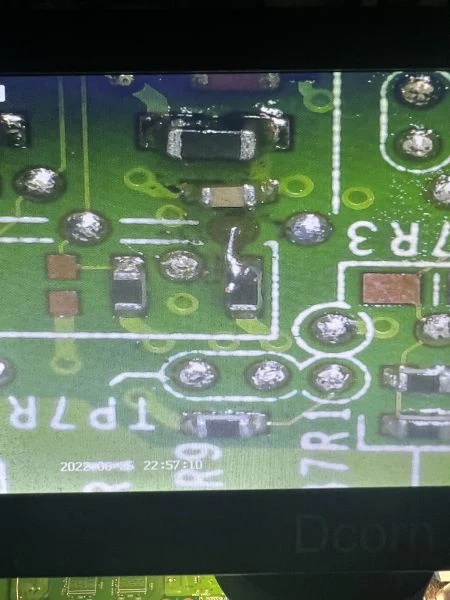
3.3v, 5v, & GND
SDA and SCL are ignored with EXT_CLK.
1.8V (Only if using an X360 ACE V1/V2/V3)
- Non-Xenon
- Xenon
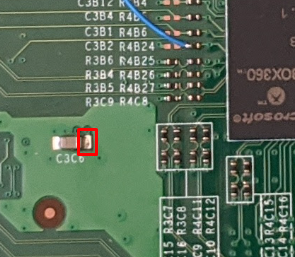
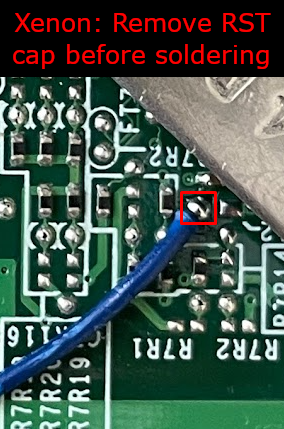
CPU_RST
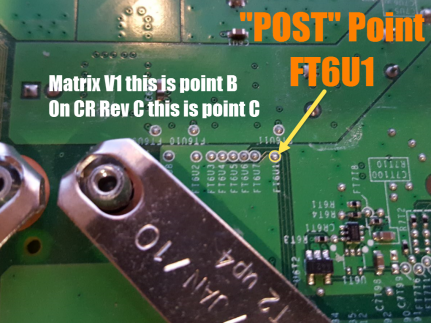
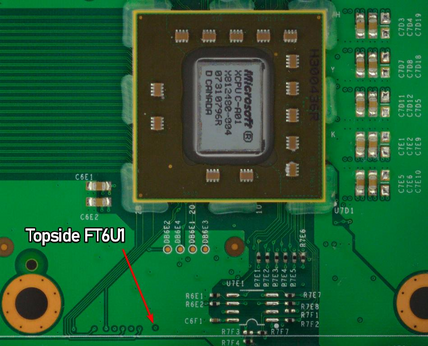
POST
- Bottom
- Top (requires scraping)
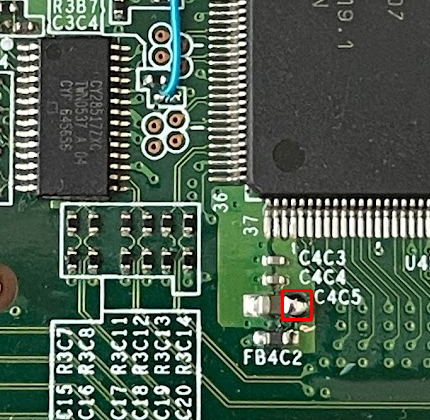
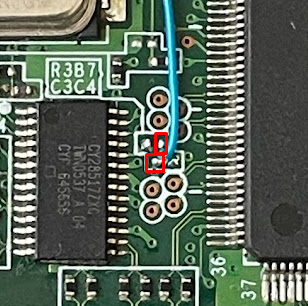
STBY_CLK
- Top (Xenon)
- Top (Non-Xenon)
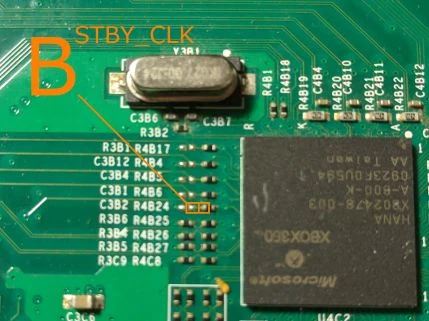
- There are 2 points boxed; either can be used.
- Bottom (Non-Xenon)
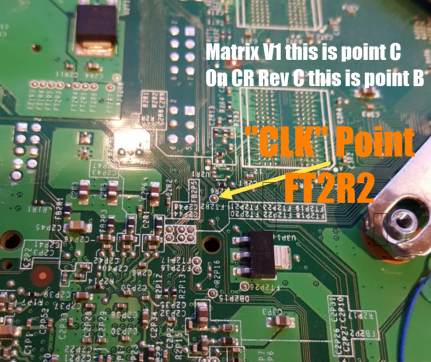
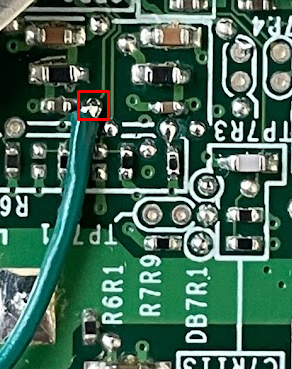
EXT_CLK
- Bottom
Glitch Chip Pinouts
Matrix
- A - RST
- B - POST
- C - STBY_CLK (remove oscillator if equipped)
- F - EXT_CLK
- If you have a Matrix that comes with an oscillator, it can be easily disabled if this resistor is removed instead of removing the entire oscillator.

CoolRunner
- A - EXT_CLK
- B - STBY_CLK (remove oscillator if equipped)
- If you have a Rev D, its built-in oscillator can be easily disabled if this resistor is removed instead of removing the entire oscillator.
- C - POST
- D - RST

X360ACE (V1/V2/V3), DGX
- C - POST
- D - RST
- E - STBY_CLK (only if not using oscillator version)
- F - EXT_CLK (22K ohm resistor required)
- Remember to remove the diode and connect 1.8V

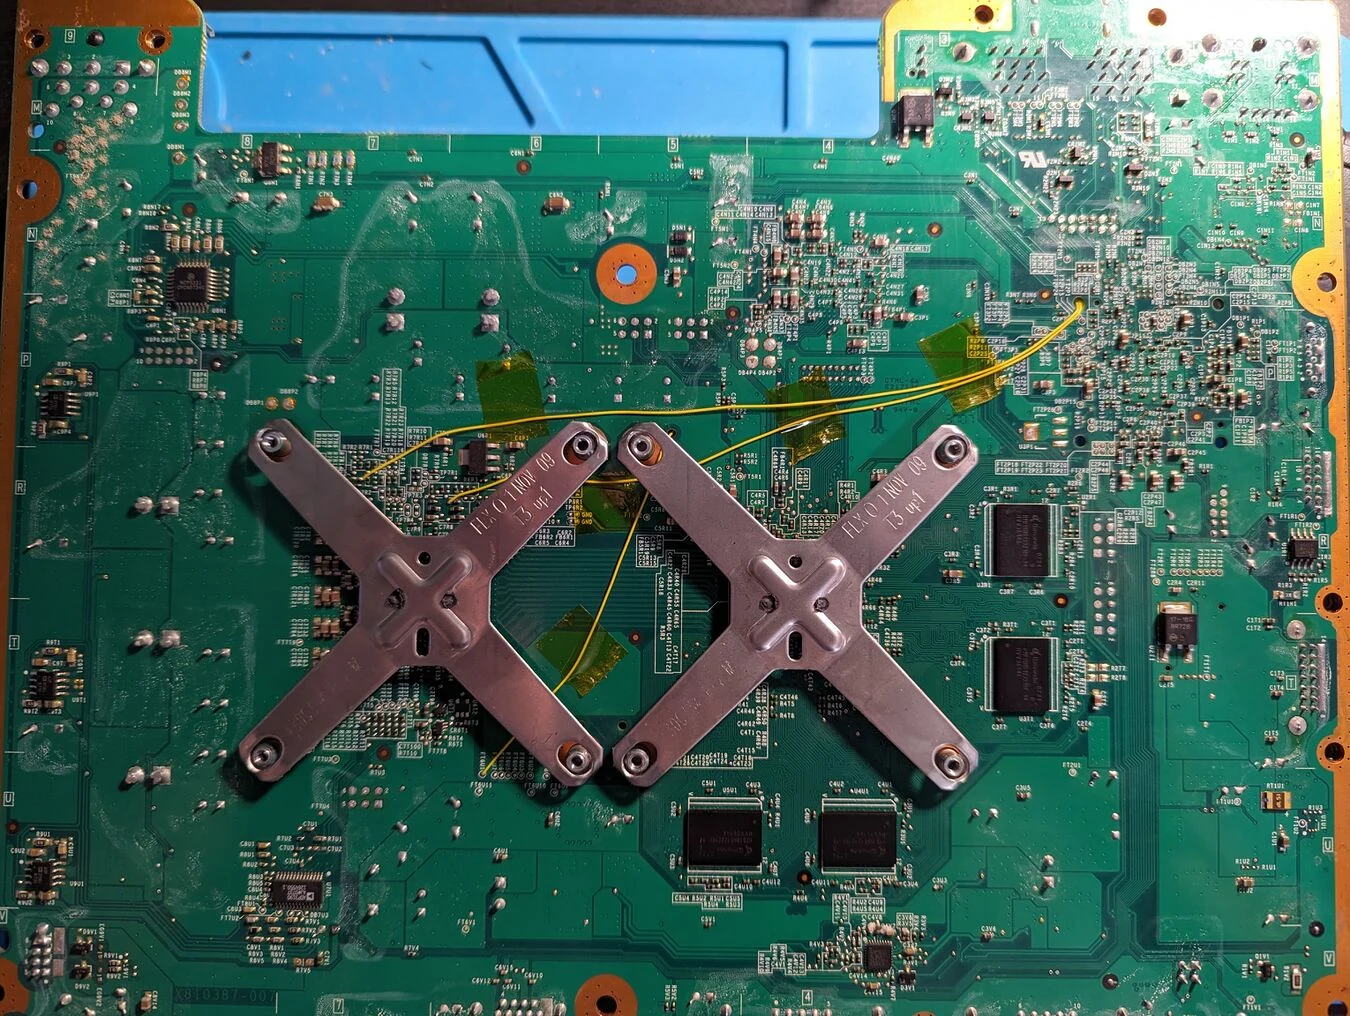
Example Installation
Bottom
Testing the Console
Once you've finished soldering, clean up any flux with isopropyl alcohol and cotton swabs. Partially re-assemble your Xbox 360, ensuring that:
- Heatsinks are attached (If they were removed for some reason)
- Fan(s) are in place and plugged in (On a phat console, the fans can be angled on top of the heatsinks to cool them for testing)
- The RF board is plugged into the front of the console
- An A/V or HDMI cable is plugged into the Xbox 360 and into a TV or monitor
- A power brick is plugged in to both the wall and Xbox 360
- (Optional) An Ethernet cable is plugged into the Xbox 360 and a LAN (e.g. a switch, router, or directly to a PC)
Turn on your console, and it should boot into XeLL Reloaded within a minute. If you don't have an Ethernet cable connected, write down (and/or take a picture of) the "CPU Key" listed on screen. If the console doesn't boot into XeLL, check all previous steps and double-check your wiring accuracy and quality.
Writing a New NAND Image
Once you have successfully booted XeLL, we can use XeBuild to make a Freeboot image with your now obtained CPU key, which is a modified version of the OS built specifically for your console.
Decrypting & Patching the NAND
- Open J-Runner and select
...next to the Load Source field and select one of your original NAND dumps if not already selected. In the upper right of J-Runner, ensure theGlitch2radio button is selected. If RGH 3 XeLL (which is the .ecc file) was written to the NAND earlier,Glitch2andRGH3should already be enabled. If not, or you used Bad Update to do a NAND dump, enable them. - Enter your CPU key into the CPU Key text field.
- The J-Runner software itself can automatically grab the CPU key of a console if both are connected to the same network. To do this, enter the IP address XeLL gives you into the lower right of the app. You can then click
Get CPU Keyand XeLL will automatically decrypt the retail NAND dump you backed up earlier. It's recommended to also click "Extract Files" in order to extract additional data from the NAND, such as your keyvault. - You can also use XeLL's built-in web server to get the CPU key; simply enter the Xbox's IP address in your preferred web browser. You will see information about the console, and the CPU key can be easily copy and pasted from this web page. It's recommended to download the keyvault as well.
- If you didn't have access to an Ethernet cable to plug the Xbox into a PC or LAN, you can manually type the CPU key into J-Runner in order to decrypt your original NAND dump.
- The J-Runner software itself can automatically grab the CPU key of a console if both are connected to the same network. To do this, enter the IP address XeLL gives you into the lower right of the app. You can then click
- Go in the
Patchestab and enable any desired options. Commonly used ones will be listed below.UsbDSecwill remove the console's security restrictions of XInput peripherals, allowing you to use various controllers or controller adapters as long as they output the XInput protocol. This is also mentioned in the Using Modern Controllers page.XL HDDandXL USBenable the ability to use USB/SATA storage larger than 2 TB, with the caveat that they have to be formatted in a special way with FATXplorer.
- Click "Create XeBuild Image". This will take a few moments, and when it's finished, it will be a
updflash.binfile in J-Runner's working directory. You can click theShow Working Folderbutton in order to quickly get to it.
NAND Flasher Method
- Power down the console and connect your programmer to the motherboard.
- If you are using an xFlasher, ensure the switch is set to
SPI.
- If you are using an xFlasher, ensure the switch is set to
- In J-Runner, select the
updflash.binXeBuild image created by the program and click "Write NAND". - Disconnect your NAND programmer from the console's motherboard and the PC when the process completes.
- Check if the console boots to the Microsoft dashboard. If it successfully boots to the dashboard, it is an indication that you've successfully hacked your console.
- Continue in the Cleaning Up section.
XeLL Method
- Copy the
updflash.binfile created by J-Runner to a FAT32 formatted USB storage device and plug it into your powered-off console. - Turn on your console. It will boot into XeLL and begin flashing your NAND. Once it has finished, it will power off your console.
- With Bad Update, you can also access XeLL with either XeUnshackle directly, or the XellLaunch application.
- Turn it back on, and it should boot to the Microsoft dashboard, which is an indication that you've successfully hacked your console.
- Tune boot times if necessary.
- Continue in the Cleaning Up section.
Simple 360 NAND Flasher Method
Since this method requires a homebrew app, it can only be done with Bad Update on a stock console.
- Unzip 360 NAND Flasher to your Xbox 360's internal hard drive or a USB drive.
- Copy
updflash.binto the directory of 360 NAND Flasher's executable. - Run the application in your desired dashboard. (e.g. Aurora, Freestyle, XeXMenu, etc.)
- Press the A button and then press START. The program will flash the new NAND image and automatically reboot the console when finished.
- Verify that everything works. Make sure you are in the latest kernel version.
- Tune boot times if necessary.
- Continue in the Cleaning Up section.
Tuning Boot Times
Boot the console several times and ensure it boots consistently. If not, make sure your wiring is clean and neat and avoids noisy areas, like any inductor coils. Run the wires near the X-Clamps for best results.
- If the light stays on at the end of a cycle:
- This means that the checks were passed, but the console failed to start
- Probably the timing is too low, or the pulse length is too large
- If the light goes off at the end of a cycle but doesn't boot:
- This means that the checks failed
- Probably the timing is too high, or the pulse length is too small
Note: Debug light behavior may be slightly misleading due to using POST_OUT bit 0.
Cleaning Up
- Remove the NAND programmer wires from the console and clean the points. Clean all flux off the board, allow it to dry, and test it once more before re-assembling.
- You may want to leave your Xbox 360 disassembled so that you can disable the eFuse-blowing circuit so you can't accidentally install official updates on your console.
Installing XeXMenu
- Plug a flash drive into your Xbox 360 and navigate to Console Settings > Storage. Select the flash drive and format it.
- Make sure you have hidden folders enabled on your PC.
- Go into
File ExplorerunderViewon top, check markHidden Items.
- Go into
- Plug the flash drive into your PC. Open the
Contentfolder, select "New Folder", and name it0000000000000000(16 zeroes). Open the new folder, make another folder under the nameC0DE9999, open that folder, and finally make one last folder called00080000The full folder path should now be0000000000000000/C0DE9999/00080000/. - Extract the
C0DE99990F586558file from the XeXMenu archive to the0000000000000000/C0DE9999/00080000/directory on the USB drive. - Safely eject your flash drive and plug it into your Xbox 360. Navigate to the Demos section of your dashboard, and it should list XeXMenu there. Select it to launch it.
- You can install XeXMenu to your hard drive by going to Console Settings > Storage and copying it from your flash drive to the hard drive.
From here, you can install any homebrew or mods that you want. See this page for a list of recommended modifications and applications to install.