- English
- português
 | Before reading this page, you may want to visit this definitions page so any term you're currently unfamiliar with can be explained. |
Over the years, Xbox 360 consoles have had several motherboard revisions. It is important to identify the motherboard revision to see what exploits are compatible and work best with your console. The steps for the mod itself will also vary depending on the motherboard. The easiest way is to look at the motherboard's PSU connector (phat) or required amperage (phat or Slim). Octal450's identification wizard is a useful & user-friendly tool for identifying an Xbox 360 motherboard. You can view the buying guide for more information on specific revisions and how to identify an Xbox 360's motherboard.
Xbox 360 ("Phat")
Softmod Information
All Xbox 360 Phat revisions that are updated to dashboard/kernel 2.0.17559 are also compatible with the Bad Update and Peer Pressure software exploits, which allow for a similar unlocked experience to consoles modified with RGH/JTAG methods.
Hardmod Information
If your console is running dashboard/kernel 2.0.7371 or lower, it will have access to the JTAG exploit. However, some Jasper consoles manufactured with 7371 were patched against the JTAG exploit, in which case their CB needs to be checked after a NAND dump. All Tonasket consoles will also have a patched CB from the factory if they still have 7371. Refurbished Xenon consoles with Elpis GPUs will also have a JTAG patched CB.
If your console's dashboard/kernel is above 2.0.7371 and/or has a patched CB, you can use various Reset Glitch Hack methods. 2.0.14699 and lower on original consoles have access to RGH 1, but anything newer is also compatible with RGH 1.2, RGH 2 (non-Xenon), RGH 3, and EXT_CLK (Xenon/Zephyr). The newer RGH methods can still be used on consoles with 14699 and older dashboard versions as well.
There is also R-JTAG which requires dashboard/kernel 2.0.14719 or higher, and R-JTOP which requires dashboard/kernel 2.0.15572 or higher. They are essentially RGH but instead of glitching the CPU directly into a custom bootloader and into a modified NAND, they glitch the LDV check of the bootloader to boot into an official JTAGable bootloader, and into a JTAG NAND. There is usually no need to use these methods over normal RGH, as they require more steps for little benefit.
Drive Flashing & ODE Information
Any DVD drive in an original console can be flashed without soldering. However, the Lite-On DG-16D2S requires a probe tool to retrieve the DVD key without exploiting the it was paired with. If the console was exploited through JTAG, RGH, or Bad Update, the DVD key can be retrieved with NAND dumping software.
All phat consoles are also compatible with ODEs, but you will need to extract the DVD key. Getting the DVD key is the same process as if you wanted to flash it.
Xbox 360 S ("Slim")
Softmod Information
All Xbox 360 S revisions that are updated to dashboard/kernel 2.0.17559 are compatible with the Bad Update exploit, which allow for a similar unlocked experience to the consoles modified with RGH methods.
The Peer Pressure exploit will also compatible on S consoles with the Trinity motherboard, but not consoles with the Corona/Waitsburg motherboards. As mentioned by its creator, Grimdoomer, it has been proposed that the updated southbridge that these motherboards use did a hardware-level mitigation to SMC exploits (ones similar to the original SMC exploit), which prevents this exploit method from working on these later motherboard revisions.
Hardmod Information
S consoles can use most RGH methods, but cannot use R-JTAG/JTOP or the original SMC JTAG exploit, since the Slim CPUs aren't compatible with JTAGable phat CB bootloaders. They also cannot use RGH 1 for similar reasons.
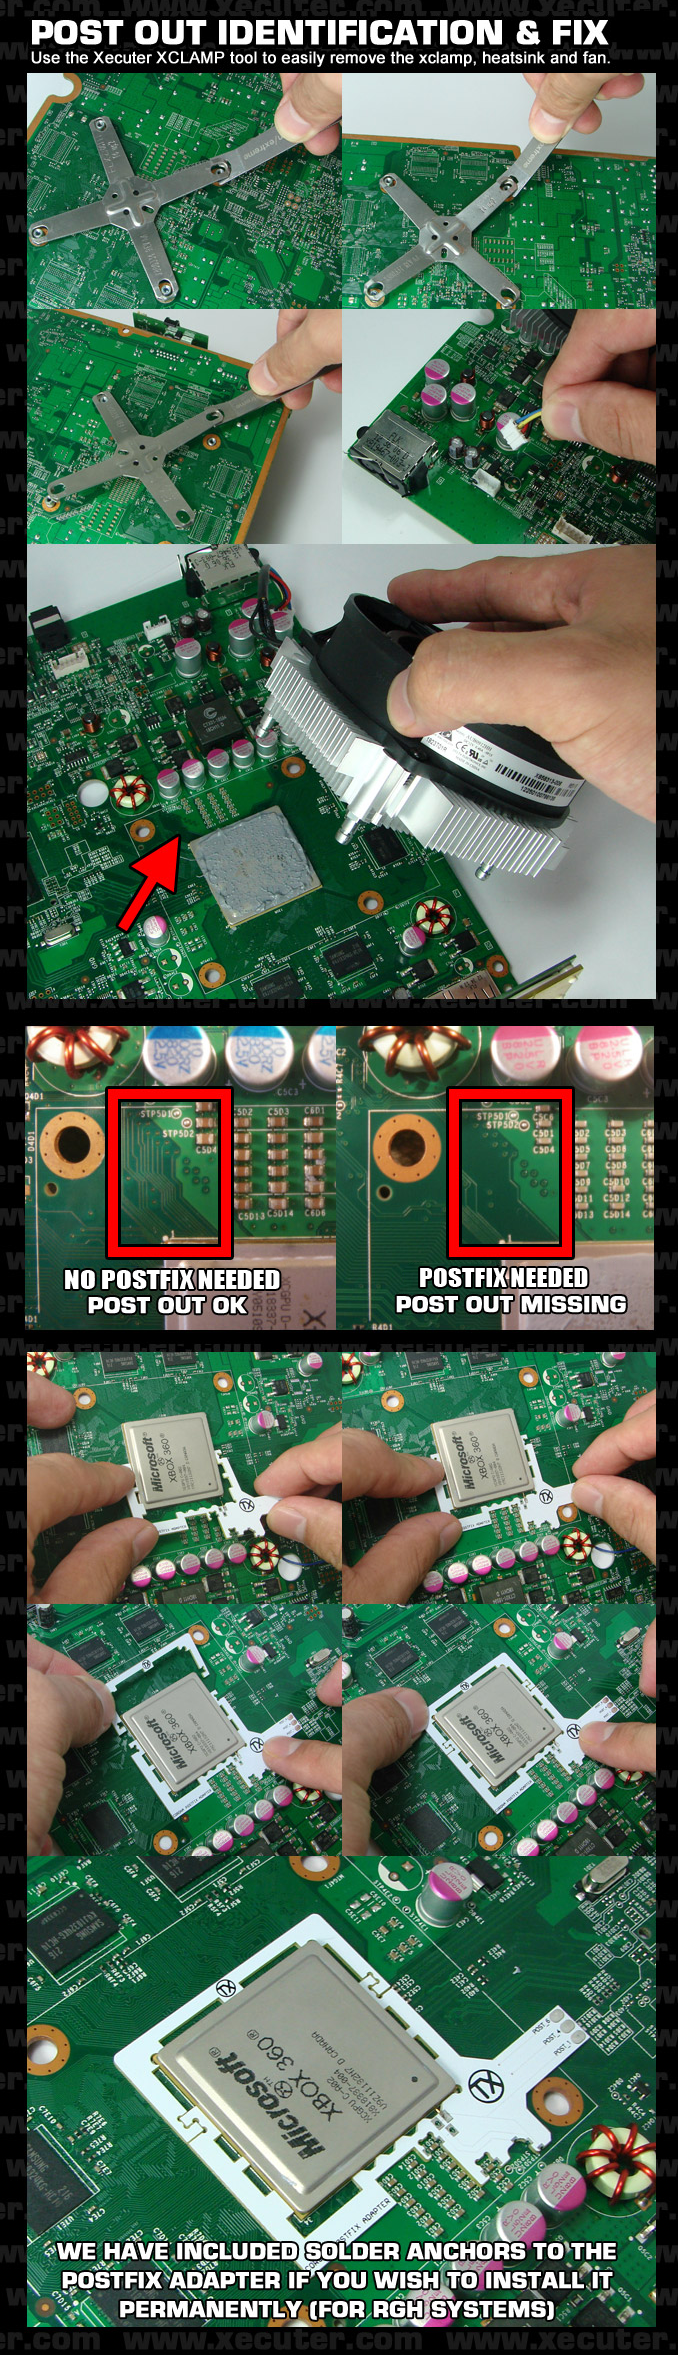
Consoles with Waitsburg motherboards also need a Postfix Adapter in order to have RGH installed, as the CPU POST lines have been removed on this motherboard revision.
Drive Flashing & ODE Information
DVD drives from S consoles are flashable if they came with a Lite-On DG-16D4S (usually came with Trinity and some early Corona consoles), but if they have a Hitachi DL10N (uncommon, but could come with any Slim console) or DG-16D5S (usually Corona/Waitsburg consoles) you need to buy an aftermarket DVD drive PCB and RGH the console to get the DVD key. The PCB in Lite-On drives also have some of the wires soldered to the PCB, but the Hitachi drives instead have ribbon cables for all connections, so replacing the PCB for a Slim Hitachi drive is easier.
- DG-16D4S drives with MXIC flash need a probe tool like the phat D2S, but uses a different type of probe tool. It must be a probe tool for a DG-16D4S. Do not use a probe tool intended for a 16D2S and vice versa.
- Some DG-16D4S drives come with a "Winbond" flash chip (example) which requires the infamous Kamikaze mod in order to flash custom firmware. It involves drilling a specific area on the chip to unlock write permissions.

All S consoles are compatible with ODE devices, but you will need to extract the DVD key. If your console has a Lite-On DG-16D5S or Hitachi DL10N, the only way to get the DVD key is to use RGH or Bad Update on the console.
Xbox 360 E
Softmod Information
Both Xbox 360 E motherboard revisions (Stingray & Barracuda) that are updated to dashboard/kernel 2.0.17559 are also compatible with the Bad Update exploit, which allow for a similar unlocked experience to the consoles modified with RGH methods.
However, the Peer Pressure exploit will not be compatible with either Xbox 360 E motherboard revision, since they have the same problem as the Corona/Waitsburg.
Hardmod Information
Stingray motherboards in the 360 E are similar to Corona/Waitsburg motherboards in 360 S, but with some features cut, like the AV port and one of the USB ports. Thus, they also need a postfix adapter like on Waitsburg Slims to utilize RGH, and have the same RGH methods available.
Barracuda motherboards (also known as "Winchester") in the 360 E are not compatible with the RGH exploit at all, due to major CPU changes that block necessary entry points used for RGH.
Drive Flashing & ODE Information
DVD drives in Xbox 360 E's are usually a DG-16D5S, which are not flashable and the DVD key cannot be extracted. The same applies to the Hitachi DL10N. It is possible to get the DVD key & OSIG with RGH (only with a Stingray console) or Bad Update (either Stingray or Barracuda), but flashing requires a PCB replacement, as the original daughter boards on these drives don't have a known exploit. S/E Hitachi drives don't have any wires soldered to the PCB, so PCB replacements for those will be easier.
Xbox 360 E's can also use ODEs, but you will still need to use RGH or Bad Update the console to get the DVD key, just like if you were replacing & flashing the DVD drive's PCB.
Choosing what kind of hack to use
Bad Update and RGH/JTAG Feature Comparison
This chart below details the features that are obtainable on both Bad Update and RGH/JTAG, so you can be informed if having an RGH console is truly necessary for you. Peer Pressure will eventually have more detailed notes on this chart, once it's publically released and its feature set can be properly evaluated versus the existing exploits.
| Feature | RGH/JTAG | Bad Update | Peer Pressure | Additional Notes |
|---|---|---|---|---|
| Requires soldering | Yes | No | No | Since Bad Update only relies on the retail operating system, nothing has to be soldered to the motherboard to make it function. All it needs is a functional console and a USB drive, and a functional Xbox 360. |
| Immediate boot into modified OS right after console is powered on | Yes | No | Yes | Since Bad Update can only be enabled after a retail console has finished booting into the unmodified OS, this is technically not a feature of Bad Update. However, due to the exploit speed of Bad Update 1.3 & ABadAvatar 1.3, this is only a minor inconvenience vs an RGH console. ABadAvatar can also automatically boot without any user input, as long as none of the profiles have auto sign in enabled. |
| Running game backups from HDD/USB | Yes | Yes | Yes | This is basically the same experience as using them on RGH/JTAG, as long as you pair Bad Update with a hypervisor patcher payload, such as XeUnshackle or FreeMyXe. |
| Running custom .xex homebrew | Yes | Yes | Yes | This is basically the same experience as using them on RGH/JTAG, as long as you pair Bad Update with a hypervisor patcher payload, such as XeUnshackle or FreeMyXe. |
| Unofficial SATA HDDs | Yes | Yes* | Yes | The modified OSes on RGH/JTAG have built-in patches to unlock SATA HDD support, so you aren't restricted to Microsoft branded HDDs that come with their matching security sector, or SSDs/HDDs modified with Xbox 360 HDD/SSD Maker in FATXplorer.
Bad Update can use this feature too, but only through a fork of Bad Storage, or by shadowbooting. The unsecured HDD also won't be accessible without any USB drive or memory unit connected that has Bad Update installed, as the console will be in the unmodified retail state. |
| DashLaunch compatability | Yes | Yes* | No | DashLaunch (a kernel patcher that adds additional features to the OS, such as loading your own plugins) was originally built for RGH/JTAG consoles, but can also be used with Bad Update with the XeUnshackle app.
DashLaunch's original GUI configurator app can potentially brick Bad Update consoles if you accidently used its NAND install feature, but this has been addressed due to its source code being released, so you can just use a patched version of the app that has all of the NAND installation/updating features blocked in order to configure your XeUnshackle's DashLaunch settings. Peer Pressure's built-in kernel patcher already provides all of DashLaunch's features except for loading custom .xex system plugins on boot, so DashLaunch isn't supported due to it being functionally redundant. |
| Stealth server plugins | Yes | Yes | TBD | Since stealth server plugins are just DashLaunch plugins, they can still be utilized on Bad Update as long as you can access DashLaunch with XeUnshackle. You may also want to install the AutoDNS plugin with them, so that Xbox Live is always blocked until you have actually finished booting info XeUnshackle.
Stealth servers at this time don't support automatically unblocking Peer Pressure's Live blocking features, but it should be easy to implement in future stealth server updates. |
| Booting Blades/NXE dashboards on 17559 | Yes | Yes | TBD | If you have access to DashLaunch plugins that can do the necessary patches to allow for the Blades/NXE dash.xex files to function on the latest 17559 kernel, then it is possible to use these old dashboard executables like if you were booting their matching kernel natively, while retaining the game compatability of 17559.
At the time of writing, this feature is only in stealth server plugins. |
| Booting development kit OS | Yes | Yes* | Yes* | While RGH consoles can directly boot into a dev kit OS from their system flash (RGLoader/XDKBuild), both Bad Update and RGH/JTAG can boot into RGLoader (a heavily modified version of the dev kit OS) from the retail OS by shadowbooting.
JTAG systems in particular may have issues with kdnet, but since JTAG exploited systems are niche in the first place, this won't be a huge issue for most, as they will opt for RGH anyway. |
| Kernel downgrading | Yes | Yes* | TBD | NAND flashing applications can be used reguardless of exploit method, but since the Bad Update exploit hasn't been ported to anything that isn't the latest 17559 kernel, it is impossible to revert a downgrade without soldering NAND flashing hardware to manually revert back. On RGH/JTAG, you can boot these same old dashboards (such as Blades and NXE) natively on the system's flash, but with Freeboot patches, which allows you to both use homebrew/game backups, and still access XeLL on the flash to revert the downgrade.
Being able to boot odd kernels, such as 1838 or 1888, are also exclusive to RGH/JTAG systems at this time. |
| Font downgrading | Yes | No* | TBD | Many users which have enthusiasm for the Xbox 360's NXE dashboard (the dashboard interface used from 2009-2010) have also discovered you can directly swap the modern font file on the system flash of an RGH/JTAG console with the old font file, with allows the console interface to have that desirable retro look. It's often paired with using the NXE dash.xex itself (so that the dashboard's appearance is more authentic to how it natively is), along with plugins (usually to allow for the old NXE dash.xex to still function on the 17559 kernel.
This feature is theoretically possible with Bad Update, but only with shadowbooting. This feature doesn't work when you try to modify the font file in the system flash of a retail 17559 console. |
| Customizable boot animation | Yes | No* | Yes | Since a Bad Update console is ultimately a retail console, and the exploit doesn't have a public entry point implementation earlier in the boot process, the boot animation that can be seen after pressing the power button can't be changed. If you attempt to do so, you will just see a black screen for 10 seconds until the dashboard loads. For what it's worth, it is also possible have a custom animation for after XeUnshackle has booted. |
| Booting XeLL directly with eject button | Yes | No | Yes | RGH/JTAG directly exploit the console's boot process, so it is possible to boot XeLL even if the normal OS can't be booted into, as XeLL can be installed on a seperate location in the NAND. XeLL can still be accessed on Bad Update, but only by booting the XeLL binary file from USB/HDD after a hypervisor patcher app was enabled.
With Peer Pressure, it has an OtherOS configuration that allows you to boot XeLL instead of the Xbox System Software with the eject button. |
| Booting burned copies of games in the disc drive | No* | No* | No* | Out of the box, the Xbox 360 isn't able to boot stealth patched backups of games burned onto dual layer DVD-Rs or DVD+Rs, even if you boot a patched OS with RGH/JTAG/Bad Update. However, if you have access to plugins, you can install the NetISO plugin to enable support of stealth patched game backup discs, just like if you had a flashed DVD drive. |
RGH/JTAG
- Various Reset Glitch Hack or JTAG methods will fully unlock the console for homebrew, emulators, unencrypted game backups, region free DVD movies/games, running Linux, running a developer kernel, etc.
- Hacks that fully unlock the console with a fully untethered persistent exploit like RGH or JTAG require soldering, and there is no software alternative at this time.
Which RGH/JTAG method should I use?
The below chart highlights the recommended hack to use on each console. Exploit Chart has a more detailed chart that shows many more RGH methods.
Systems that are compatible with JTAG are expensive and hard to find, so generally speaking, you should just look into RGH.
| Dashboard | Xenon | Zephyr | Falcon/Opus1 | Jasper | Tonasket4 | Trinity | Corona | Barracuda (AKA Winchester)5 |
|---|---|---|---|---|---|---|---|---|
| ≤73712 | JTAG | JTAG | JTAG | JTAG | N/A | N/A | N/A | N/A |
| >7371 | EXT_CLK | EXT_CLK | RGH1.2 | RGH1.2 | RGH1.2 | RGH1.23 or RGH33 | RGH1.23 or RGH33 | N/A |
1 Opus is just Falcon without HDMI, so they are grouped together.
2 Must check CB via NAND dump to see if it is JTAGable. Most, but not all consoles on 7357, 7363, and 7371 may've came with a patched CB from the factory, whereas any Blades console is guaranteed to not have a patched CB. This mainly effects Jasper systems, as some were manufactured with a patched CB when brand new.
3 Requires scraping solder mask off of a tiny point (more difficult). S-RGH is a viable alternative that has easier soldering.
4 Tonasket consoles are essentially a Jasper with a Kronos GPU. RGH methods are the same but are never JTAG exploitable due to all of them shipping with patched bootloaders.
5 Barracuda doesn't have a known hardware exploit available, so your only option is a software exploit like Bad Update.
Peer Pressure
- Fully software-based exploit, all you need is a USB stick and a SATA hard drive.
- Works on any phat 360 model (including Xbox 360 S Trinity models, but not Corona or newer) running dashboard 17559 (the latest as of this writing).
- Persistent exploit; Peer Pressure is automatically run almost instantly after turning the console on.
- Has minor limitations compared to RGH or JTAG, but can run homebrew and game backups the same way.
Bad Update
- Fully software-based exploit, all you need is a USB stick.
- Works on any 360 model (including Barracuda [Winchester] models) running dashboard 17559 (the latest as of this writing).
- Non-persistent, has to be re-run every time you turn the console on, exploit enables nearly instantly after it is run, and sometimes (but rarely) fails (has a success rate of ~90%)
- Has minor limitations compared to RGH or JTAG, but can run homebrew and game backups the same way.
DVD Drive Flashing
- An Xbox 360 with a DVD drive flashed with custom firmware will allow you to play retail game backups with burned DVDs, but will not allow access to homebrew, emulators, game mods, backups of digital games, or even a region unlock.
- DVD drive flashing with any phat or a Slim DG-16D4S DVD drive does not require any soldering, unlike JTAG or the Reset Glitch Hack.
Optical Disc Emulator
- The Xbox 360 had a few optical disc emulators released for it, such as the XK3Y ODE, Wasabi360, and Boxzii. These devices allowed you to play .iso dumps of retail games through USB or eSATA storage.
- ODEs have not been manufactured in a long time, and were expensive. Similarly to a flashed DVD drive, these didn't unlock the console for unsigned software and were only used for playing disc backups. They tend to not be very common on the used market, either.
King Kong Exploit
| This hack is not recommended as it is very limited and only for very old dashboards. It is just listed here for completeness. |
- The King Kong exploit used a modified copy of Peter Jackson's King Kong to allow the Xbox 360 to boot into a Linux distribution. The KK exploit didn't allow access to homebrew outside of Linux. An application like XeUnshackle could theoretically run on the King Kong exploit, but this hasn't been developed, and has little interest due to how rare the compatible consoles are.
- This exploit did not permanently modify the console's operating system, and the game had to be loaded every time you wanted to use Linux.
- Since the exploit relies on booting a modified game, the console either needed a DVD drive with modified firmware or a hot swap method in order to boot it.
- The King Kong Exploit only worked on consoles with a 2.0.4532 or 2.0.4548 kernel/dashboard, and there's no method to downgrade a retail Xbox 360 to a kernel vulnerable to the KK exploit due to the CPU's eFuses.